Claude Code Extension Backdoor on Cursor: Are You Affected?
On October 29, 2026, a tampered build of Anthropic's Claude Code extension was served to Cursor users through Cursor's own extension marketplace for about 11 hours. The build, versions 2.1.312 and 2.1.313 for macOS and Windows, added an attacker's SSH key, tried to open a reverse SSH tunnel and installed itself to run at every login. Cursor says at most 5,000 users were affected. If you use Claude Code inside Cursor, check your machine even if the extension has since updated, because updating or uninstalling does not remove what the payload left behind.
Anthropic says its own systems were not breached and that copies on its official channels, Open VSX and the Visual Studio Marketplace, were never modified. The weak point was the layer Cursor runs between those registries and its editor.
Key takeaways
- A malicious
Anthropic.claude-codebuild, versions 2.1.312 and 2.1.313, was published to the Cursor VS Code Extension Marketplace and was live from about 2:27am to 1:35pm PT on October 29, 2026 (Cursor security notice). - It reached Cursor users on macOS and Windows who received that update. Cursor said at most 5,000 users were affected and that it would contact them directly (Help Net Security).
- Not affected: Claude Code from Open VSX, the Visual Studio Marketplace, Anthropic's own hosts and the Claude Code CLI (The Register, OpenSourceMalware).
- The payload planted an SSH key with the comment
svc-telemetryinauthorized_keys, a reverse tunnel to134.209.82[.]225, persistence at login, and a one-time beacon with host details and the names (not values) of secret-looking environment variables (Phorion). - Removing or updating the extension does not clean the machine. Remove the key, the persistence entries and the tunnel, then rotate credentials reachable from the machine.
What happened to the Claude Code extension on Cursor
Cursor is a fork of VS Code. Microsoft's Visual Studio Marketplace terms only allow Microsoft's own products to use it, so forks get extensions elsewhere. Cursor's documentation says extension search and downloads go through its own service, marketplace.cursorapi.com, which draws on Open VSX, the open-source extension registry run by the Eclipse Foundation, but is "not a direct passthrough" to it (Cursor docs). That proxy is where the tampered build appeared.
According to Cursor's notice, published October 29 and updated October 30 at 11:30am PT:
- The malicious versions were
Anthropic.claude-code2.1.312 and 2.1.313 for Windows and macOS. - They were live in the Cursor VS Code Extension Marketplace between about 2:27am PT and 1:35pm PT on October 29, 2026 (09:27 to 20:35 UTC).
- "These malicious versions of the extension were not developed by Anthropic."
- Cursor removed the versions on detection, audited access and found no other tampered extensions, rotated its keys, rebuilt the marketplace and brought it back online, and worked with the hosting provider to take the attacker's server offline.
The first notice named only 2.1.313. The October 30 update added 2.1.312 and revised the file hashes. Some early write-ups still list only one version or label the hashes differently, so use Cursor's current notice as the reference.
Anthropic's Felix Rieseberg told The Register that "it wasn't a compromise of Anthropic's systems or employee laptops" and that "a malicious actor used access to Cursor's marketplace to publish a tampered copy." He added: "The versions on our official channels are not affected, and this only impacts Cursor users." Another Anthropic engineer, David Dworken, wrote on Hacker News that 2.1.313 was never published to Open VSX, the VS Code Marketplace or Anthropic's hosts, and that the next release was numbered 2.1.314 to avoid confusion.
How the attacker got publishing access to Cursor's marketplace has not been disclosed.
Was Open VSX compromised?
No. Several early reports, including one advisory whose URL still says "vsx-compromise," blamed Open VSX. Those reports were corrected after Cursor confirmed its own marketplace was the source. The Open VSX API lists versions 2.1.310, 2.1.311, 2.1.312, 2.1.314 and 2.1.316 for Claude Code, and no 2.1.313. StepSecurity found the 2.1.312 build on Open VSX clean (StepSecurity). The 2.1.312 that Cursor flags is a different file served by Cursor's marketplace, which is why the version number alone does not settle whether you are affected.
What the backdoor did
Security firms Phorion, StepSecurity and OpenSourceMalware took the build apart. The attacker added a 66-line loader to the top of the extension's minified extension.js and left the rest of the real code in place (OpenSourceMalware). The loader runs when the editor loads the file, before the extension's own startup code, so no click was needed (Phorion).
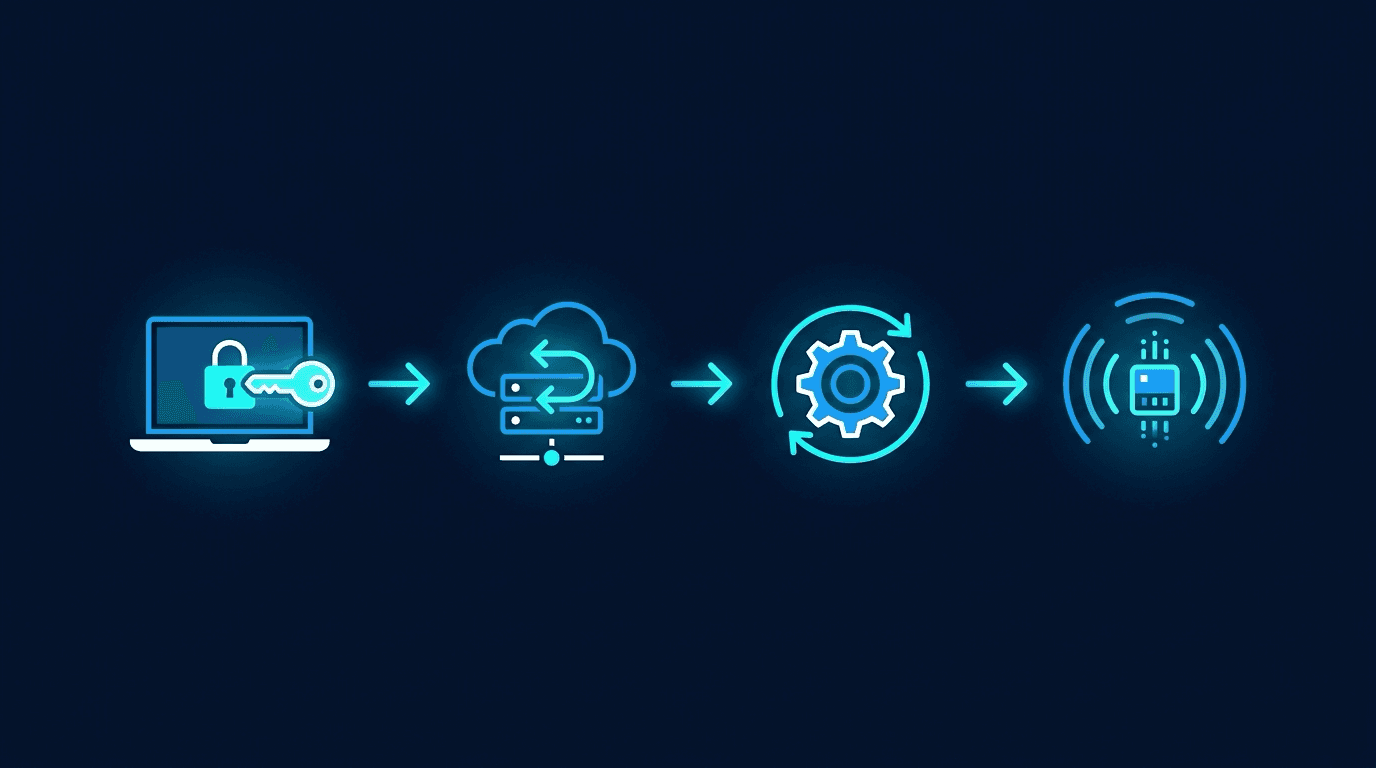
The payload worked in four steps:
- Plant a key. It appended an Ed25519 public key with the comment
svc-telemetryto~/.ssh/authorized_keys, creating the file if needed. - Try to enable SSH and open a tunnel. It tried to turn on the SSH server (Remote Login on macOS, OpenSSH Server on Windows,
sshdon Linux), then connected out totunnel@134.209.82[.]225on port 22 and asked for a remote port forward (-R *:0:localhost:22). That gives the operator a path back into the machine's SSH server without any inbound firewall opening. It retried every 60 seconds and usedautosshwhen present. - Persist. On macOS it installed a LaunchAgent named
com.apple.sysmond.plistthat runs~/.config/.smt. On Linux it added an@rebootcrontab entry. On Windows it created a scheduled task calledSysMon, or asysmon.cmdscript in the Startup folder when it lacked admin rights. - Beacon once. It sent one HTTP POST to port 8099 with the hostname, username, OS, architecture, home and working directories, global Git email, public IP and up to 40 environment variable names matching
KEY,TOKEN,SECRET,PASS,AWSorGCP. Values were not sent.
Two details limit the damage. Turning on SSH needs admin rights, and Cursor said that step would likely fail "outside of highly unusual circumstances where Cursor was started with administrator privileges" (BankInfoSecurity). On macOS, Phorion found a bug in the script's status check that usually skips the enable step for standard users. The key, the persistence and the beacon still ran, so a Mac that already had Remote Login on, or turns it on later, is exposed. Cursor says the attacker's server is now offline.
| Platform | Persistence | Files to look for |
|---|---|---|
| macOS | LaunchAgent com.apple.sysmond.plist | ~/.config/.smt, ~/.config/.smtk, $TMPDIR/.stk_* |
| Linux | @reboot crontab entry | ~/.config/.smt, /tmp/.stk_* |
| Windows | Scheduled task SysMon or Startup sysmon.cmd | %USERPROFILE%\.config\smt.cmd, smtk, %TEMP%\.stk_* |
Sources: Phorion, Cursor security notice
How to check if you are affected
You are in scope if you run Cursor on macOS or Windows with the Claude Code extension installed and Cursor was open, with extension auto-update on, during the window on October 29. If you only use the Claude Code CLI or the extension in Microsoft VS Code, the reports say you are not affected.
Then look for these artifacts, all listed in Cursor's notice or Phorion's advisory:
- SSH key: look for
svc-telemetryin~/.ssh/authorized_keys. On Windows, also checkC:\ProgramData\ssh\administrators_authorized_keys. The planted key's fingerprint isSHA256:0Z6R+DF64Do2nwQic8a7kkfDLNNk4IiK+2U2Rci4htk. - Extension folder: look for
anthropic.claude-code-2.1.312-*oranthropic.claude-code-2.1.313-*under Cursor's extensions directory. The maliciousextension.jshas SHA-256ecb58cb29078d9646ad1dcdbe51526f2d9cfea06be5fb2ab183e8ecc3ab6bf15. - Persistence: the LaunchAgent, crontab entry or scheduled task in the table above.
- Processes:
sshorautosshrunning with-R *:0:localhost:22. - Network: outbound connections to
134.209.82[.]225on ports 22 or 8099. - Use of the tunnel: SSH log entries for logins from
127.0.0.1or::1with thesvc-telemetrykey. Phorion notes these would mean an operator actually came in through the tunnel.
Cursor attached two scripts to its notice: remediate-macos.sh, run as the affected user and not as root, and remediate-windows.ps1, run as administrator. Both exit with a non-zero code if anything is left.
How to clean up
Cursor's notice and Phorion's advisory give the same order:
- Isolate hosts that show signs the payload ran. If you have endpoint tooling, save evidence before deleting anything.
- Stop the tunnel: kill the retry loop and any
sshorautosshprocess going to the attacker's address. - Remove persistence: unload and delete the LaunchAgent, remove the crontab line, or delete the
SysMontask and Startup script. Delete.smt,.smtkand.stk_*. - Remove the key with the
svc-telemetrycomment fromauthorized_keys, and turn Remote Login back off if you did not enable it yourself. - Rotate credentials reachable from that machine: Git hosting, CI/CD, cloud, package registry and SSH keys. Do it from a clean device. The beacon only sent variable names, but anyone who reached the machine through the tunnel could read the values.
- Reinstall Claude Code at 2.1.314 or later. Open VSX showed 2.1.316 as the newest version on October 31.
Uninstalling the extension does not undo steps 1 to 3 of the payload. Auto-updating to a clean version does not either, because the dropped scripts run on their own.
Why this incident matters for AI coding tools
Two things make this case different from a typical malicious extension.
First, there was nothing to spot. Many earlier attacks relied on look-alike names. Here the extension ID, publisher and name were all real. As Ax Sharma of Manifold Security put it, "Checking the publisher name doesn't help when the publisher is real" (Help Net Security). The trust chain broke at the distributor.
Second, editor forks add a distribution layer. A VS Code fork cannot use Microsoft's marketplace, so it relies on Open VSX, its own proxy, or both. Cursor's docs warn that the same publisher.extension ID can point to different publishers or code in different marketplaces. Each layer is another place where a build can be swapped. Open VSX itself dealt with the GlassWorm campaign in October 2025, reported by Koi Security. The Eclipse Foundation, which runs Open VSX, traced it to publishing tokens that developers had leaked and then added token prefixes, shorter token lifetimes and scanning at publish time (Eclipse Foundation).
AI coding extensions are a rich target because they run with the developer's full permissions next to source code, cloud credentials and SSH keys. This is the second developer supply chain incident on our radar this month, after the LiteLLM PyPI compromise, where a poisoned package release reached build systems the same way.
For teams, the practical steps are the same as for any package supply chain:
- Pin or allowlist extension versions on managed machines, and turn off auto-update where you can review updates first.
- Watch for IDE helper processes writing to
~/.ssh/authorized_keysor creatingcom.apple.*LaunchAgents. Phorion notes the key was written with Node's file API, so rules that only watchechoorteewould miss it. - Keep long-lived secrets out of shell environment variables on developer laptops.
FAQ
Which Claude Code extension versions were malicious?
Cursor lists Anthropic.claude-code 2.1.312 and 2.1.313 for Windows and macOS, as served by the Cursor VS Code Extension Marketplace on October 29, 2026. The 2.1.312 build on Open VSX is a different file and was found clean. Version 2.1.314 and later are safe.
Was the Claude Code CLI or the VS Code Marketplace version affected?
No. Anthropic said the versions on its official channels were not affected and that the incident only impacts Cursor users. Researchers reported that the npm CLI package was not malicious and that 2.1.313 never existed on Open VSX or the Visual Studio Marketplace.
How many people were affected?
Cursor said at most 5,000 users were affected and that it would contact them directly. No one has published how many machines actually ran the payload or how many tunnels the attacker used.
Does uninstalling the extension remove the backdoor?
No. The payload writes an SSH key, standalone scripts and a login item or scheduled task that keep running without the extension. Remove those by hand or with Cursor's remediation scripts, then rotate credentials.
Did the attacker steal API keys or tokens?
The beacon sent only the names of environment variables that looked like secrets, not their values. If the reverse tunnel connected while SSH was enabled, though, the operator could log in as you and read anything you can. Rotate credentials as a precaution.
Sources
- Cursor: Security notice on malicious Anthropic.claude-code 2.1.312 and 2.1.313
- Cursor docs: Extensions and the Cursor marketplace
- Phorion: Official Claude Code extension compromise advisory
- StepSecurity: Trojanized Claude Code extension delivered a persistent SSH backdoor
- OpenSourceMalware: Trojanized Claude Code extension plants persistent SSH backdoor
- The Register: Anthropic says Claude Code extension compromise wasn't on its side
- Help Net Security: Claude Code extension poisoned with persistent SSH backdoor
- BankInfoSecurity: Cursor confirms Claude Code extension compromise
- Hacker News: comment by Anthropic's David Dworken
- Open VSX: Anthropic.claude-code version list
- Koi Security: GlassWorm on Open VSX
- Eclipse Foundation: Open VSX security update, October 2025